
Stop guessing. Score every threat.
The OFA Crime Score assigns a 0–1000 risk value to every IP, domain, URL, and file hash in the Alliance ecosystem — powered by six validation layers and 290+ member organisations.
Higher scores mean stronger, multi-source confirmation
Use the bands below to calibrate your enforcement policy.
| Range | Band | Recommended Action |
|---|---|---|
| 0–80 | Clean / Unobserved | No enforcement action recommended |
| 80–140 | Watchlist / Monitor | Logging and alerting only |
| 140–250 | Block Recommended | Start at ≥400 for a safe initial deployment, then lower toward 190 |
| 250–1000 | Immediate Block | High-confidence, multi-sector confirmed — immediate enforcement |
Most organisations start at 400 and lower the threshold toward 190, the optimal block threshold, as confidence grows.
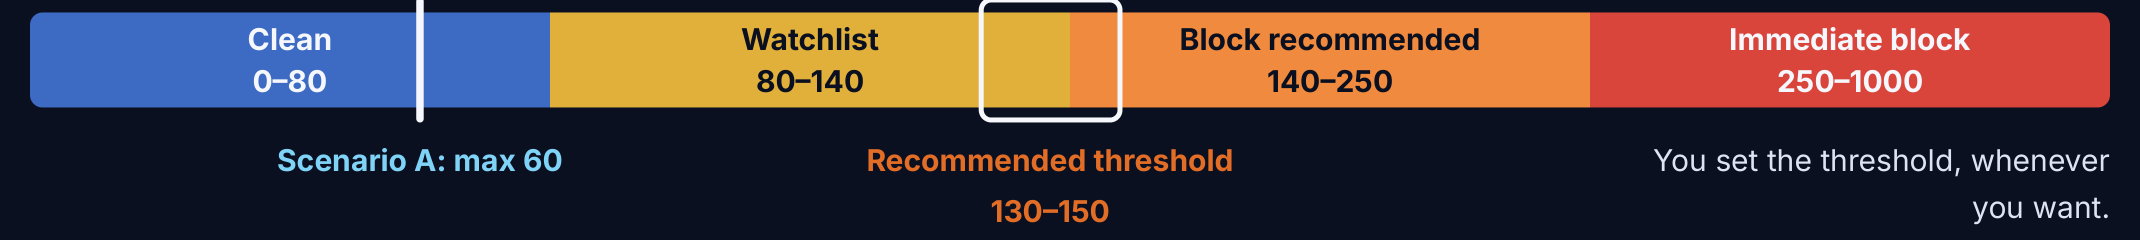
Automatic blocking, only when it's certain
It's not how often an IP attacks that counts — it's how many trusted members confirm it.
A single member, attacked 10,000 times
Volume is not enough: a single reporter, however noisy, never triggers a block.
Crime Score max 60 · not blocked
At least 4 high-trust members, in the last 2 hours
Independent sources, each given a trust level by OneFirewall, confirm the same threat actor.
Above threshold · blocked automatically
You set the threshold, whenever you want.
Every score, fully explained
Every lookup returns not just the score, but the confidence level, how many independent members reported it, and the specific MITRE techniques observed.
GET /api/v1/score?ip=185.220.101.45
{
  "ip": "185.220.101.45",
  "score": 847,
  "band": "IMMEDIATE_BLOCK",
  "confidence": 0.94,
  "members_seen": 23,
  "components": {
    "alliance_freq": 340,
    "trust_weight": 180,
    "confidence_meta": 165,
    "stix_enrichment": 100,
    "temporal_decay": 62
  },
  "mitre_ttps": ["T1190", "T1133"],
  "tags": ["tor-exit", "brute-force"]
}
No single signal determines the score
Alliance Member Frequency
Multiple independent organisations reporting the same asset increases the score nonlinearly — a dozen confirmations raises certainty.
Source Trust Weight
Each contributing member is weighted by their historical accuracy and false-positive rate.
Confidence Metadata
Per-submission confidence ratings feed directly into the composite score.
STIX Enrichment
Structured context from STIX bundles adds weight where corroborating detail exists.
Temporal Decay
Scores age naturally as sightings become less recent, reflecting infrastructure churn.
Sector Weighting
Targeting patterns across industries adjust relevance for your specific sector.
Crime Score FAQ
What is the Crime Score?
The OFA Crime Score is a 0 to 1000 risk value assigned to every IP, domain, URL and file hash in the Alliance ecosystem. It is built from six scoring components and validated by 290+ member organisations.
Does one high-volume reporter trigger a block?
No. Volume alone is not enough. A single member, however noisy, never triggers a block. A block needs independent, high-trust members to confirm the same threat within a time window, for example at least four in the last two hours.
What do the score bands mean?
Scores from 0 to 80 are clean or unobserved, 80 to 140 is watchlist (logging and alerting only), 140 to 250 is block recommended, and 250 to 1000 is immediate block for high-confidence, multi-sector confirmed threats.
Can I set my own blocking threshold?
Yes. Start at 400 for a safe initial deployment, then lower the threshold toward 190, the optimal block threshold, as confidence grows.