
Telecom-scale traffic needs retrospective intelligence, not just a perimeter rule.
Telecom Italia (TIM) has been part of the OneFirewall Alliance's intelligence pool alongside the finance, defence, energy, and technology members on this page, at a traffic volume few other sectors deal with.
Volume hides what a single rule can't catch
- Always-on by regulatory and commercial requirement. Network operators don't get a maintenance window for the core of their business the way an application team might. Availability targets here sit at the top end of any sector's requirements.
- Volume that outpaces manual review. At carrier scale, the sheer volume of flows makes it impractical to review perimeter decisions one by one. A threat that gets through once can keep getting through until something re-checks the historical record.
- NIS2 applies directly. Telecoms are explicitly in scope as part of the EU's digital-infrastructure sector under NIS2, with the same mandatory incident-reporting and accountability requirements as energy and finance.
- A single blind spot is a network-wide blind spot. Because telecom infrastructure underpins everything that rides on top of it, an indicator missed at the network layer doesn't stay contained to one application or customer.
Re-checking traffic you already allowed
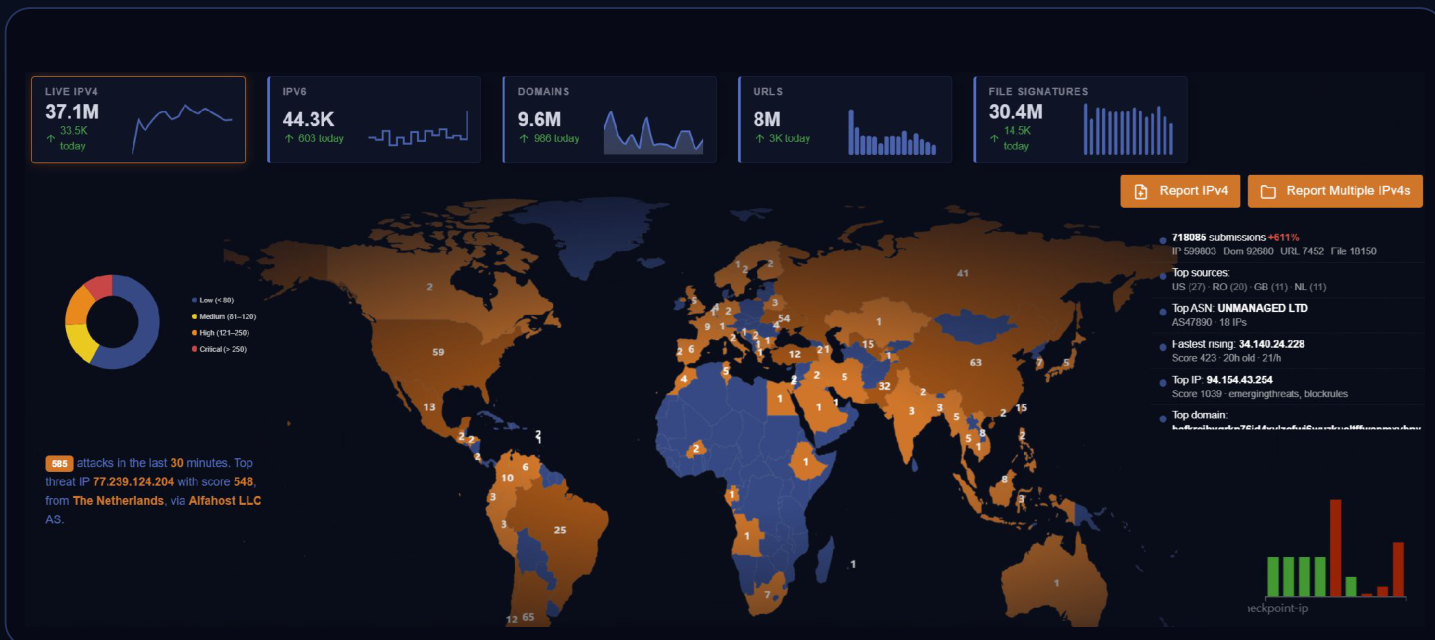
OneFirewall's NetFlow Security Analysis cross-references previously allowed traffic against the alliance's live threat-intelligence database, surfacing connections that looked clean at the time but have since been identified as malicious. That's the pattern that matters most at telecom scale, where a single missed indicator can sit in allowed traffic for a long time before anyone notices.
Enforcement at network scale, not application scale
- 166+ integrations across firewall, IPS and cloud. The WCF Agent pushes enforcement-ready intelligence into the firewalls and routers already deployed across a carrier network, no new hardware required.
- Enterprise-grade reliability. A three-node clustered deployment is available to push platform availability from the standard 99.99% toward four to eight nines for operators whose own uptime commitments demand it.
- STIX/TAXII native delivery. Intelligence is delivered in STIX 2.1 / TAXII 2.1, dropping directly into the SIEM and SOC tooling carrier-scale security teams already run.
Scale, integration, and reporting — answered directly
Our flow volume is enormous — does this actually keep up?
Retrospective analysis is built for exactly this: rather than trying to inspect every packet in real time, NetFlow Security Analysis re-checks previously allowed traffic against the live threat database, so scale works in its favour rather than against it.
Do we need to rip out our existing routers and firewalls?
No. The WCF Agent pushes enforcement into the 166+ firewall, IPS, and router platforms already supported — it's an intelligence layer on top of what's deployed, not a replacement programme.
Does this help with our NIS2 incident-reporting obligations?
Intelligence and enforcement decisions are delivered and logged natively in STIX 2.1 / TAXII 2.1, giving you an auditable record of what was detected and blocked — the kind of documentation NIS2's reporting requirements expect.