Stop defending alone.
Aggregate, validate, and consume cyber threat intelligence identified by 290+ alliance members and partner organisations. Convert distributed detection into centralised, automated blocking across firewalls, IPS, WAF, SIEM, and cloud controls.
Premium, actionable cyber threat intelligence
Every member of the alliance both consumes and contributes. The result is an intelligence graph built from real, first-hand detections — not just public blocklists — enriched and scored before it ever reaches your controls.
- Aggregated and enriched intelligence feeds across IPs, domains, URLs, and malware
- Crime Score risk rating applied to every indicator, updated in real time
- Designed for direct firewall, IPS, WAF, and SIEM enforcement
- Reduces reliance on multiple overlapping threat feed vendors
- Built for SOC teams and MSSPs operating at scale
IP Addresses
Live reputation feed
Domains
Malicious & C2 infrastructure
URLs
Phishing & malware delivery
Malware
Signature & behavioural feed
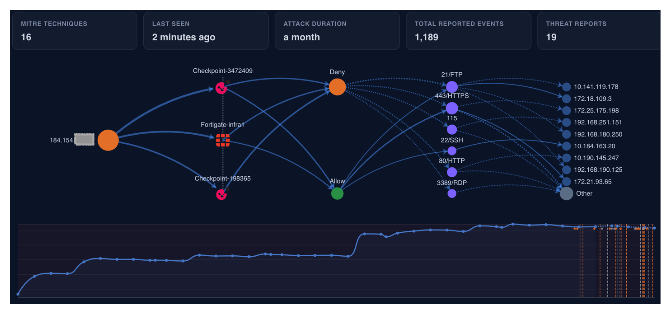
One malicious IP, seen by 19 independent members
A single-vendor firewall only sees traffic hitting its own customers. This is a real indicator from the alliance graph — corroborated by a telecom, a financial service, an automotive company, a cloud provider, and 15 other independent organisations across multiple countries, none of whom run the same firewall vendor.
Intelligence capabilities built for enforcement, not just visibility
IP Reputation Feeds
Continuously scored reputation data across every IP observed attacking an alliance member, cross-referenced against community reports.
Botnet Tracking
Live tracking of botnet infrastructure and command-and-control activity surfaced across the alliance network.
Malicious ASN Detection
Autonomous system-level risk scoring to identify hosting providers and networks disproportionately linked to abuse.
Threat Actor Monitoring
Attribution and tracking of known threat actor infrastructure, mapped against MITRE ATT&CK techniques.
IOC & CTI Automation
Machine-readable indicators delivered continuously — no manual export, no stale CSVs, no copy-paste playbooks.
Real-Time Distribution
Delta-based sync to every connected enforcement point, keeping every member firewall current within minutes.
The live views your team would actually work from
From raw IOC lookups to alliance-wide attack telemetry.
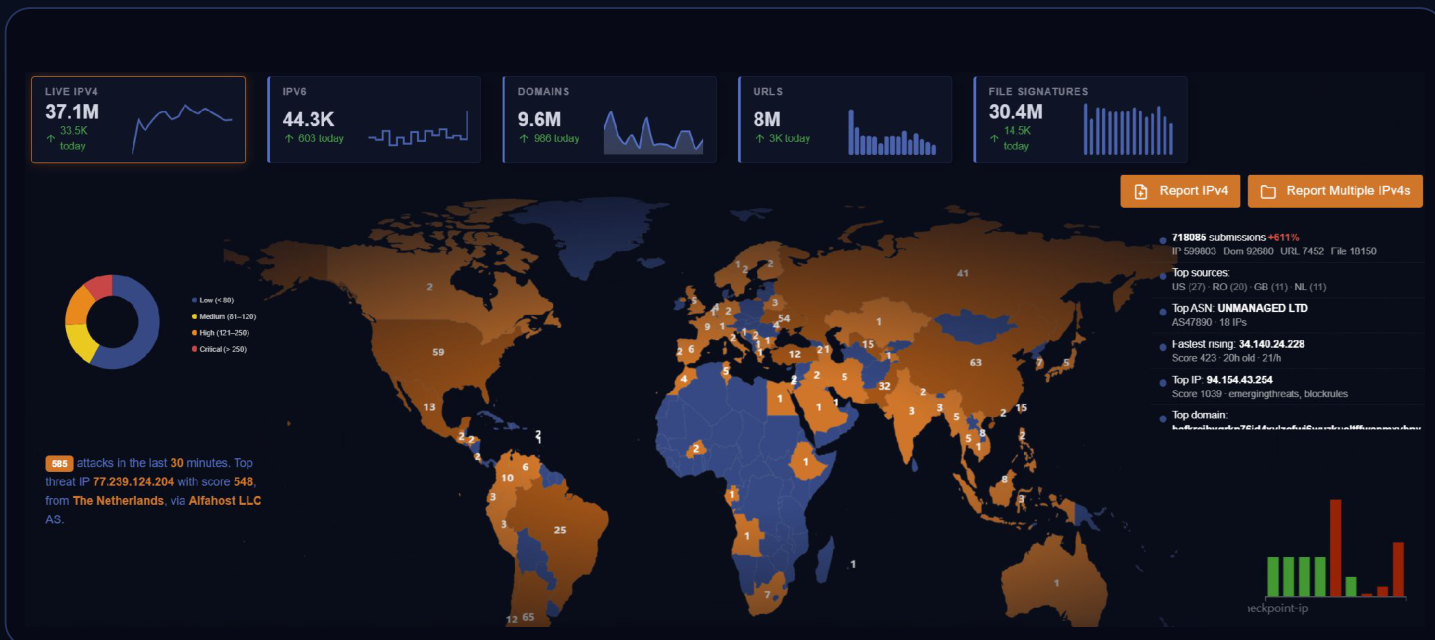
37.1M
Live IPv4 · 44.3K IPv6
9.6M
Malicious domains
8M
Malicious URLs
30.4M
Malicious file signatures
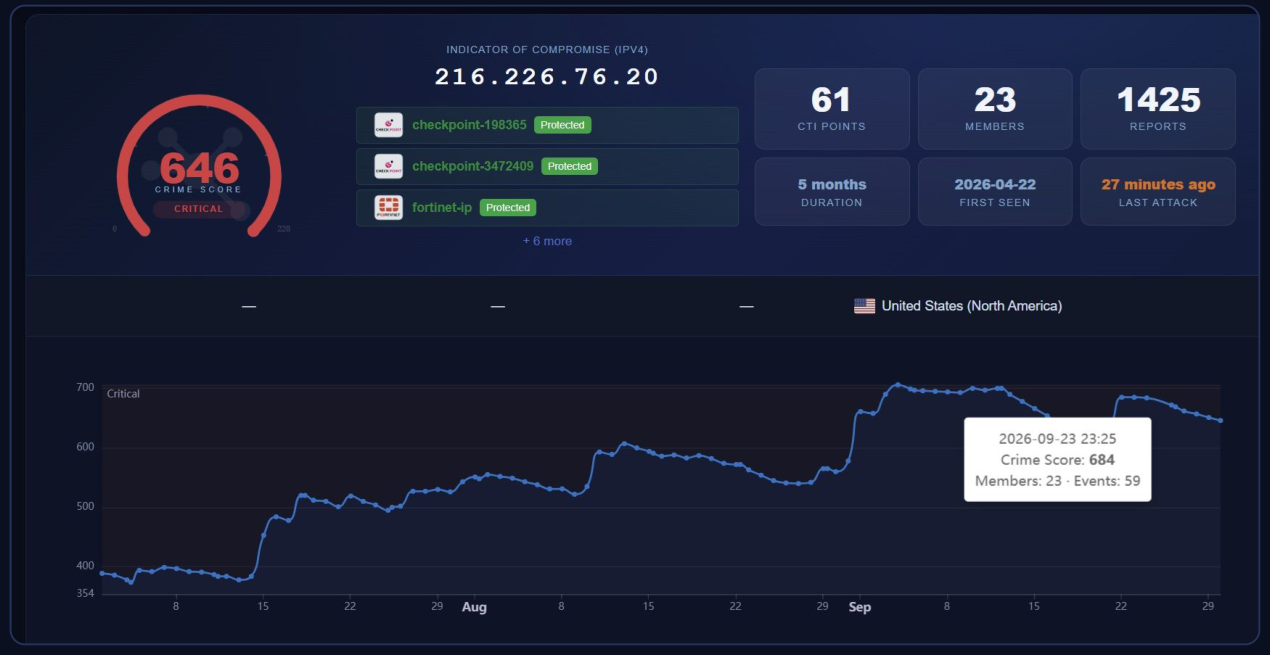
Crime Score over time, not just a snapshot
A single IPv4 cross-referenced against thousands of community reports, with its Crime Score, trend history, reporting members, and first-seen/last-attack timestamps surfaced in one view — before it ever reaches your firewall.
Every attack, mapped to a technique
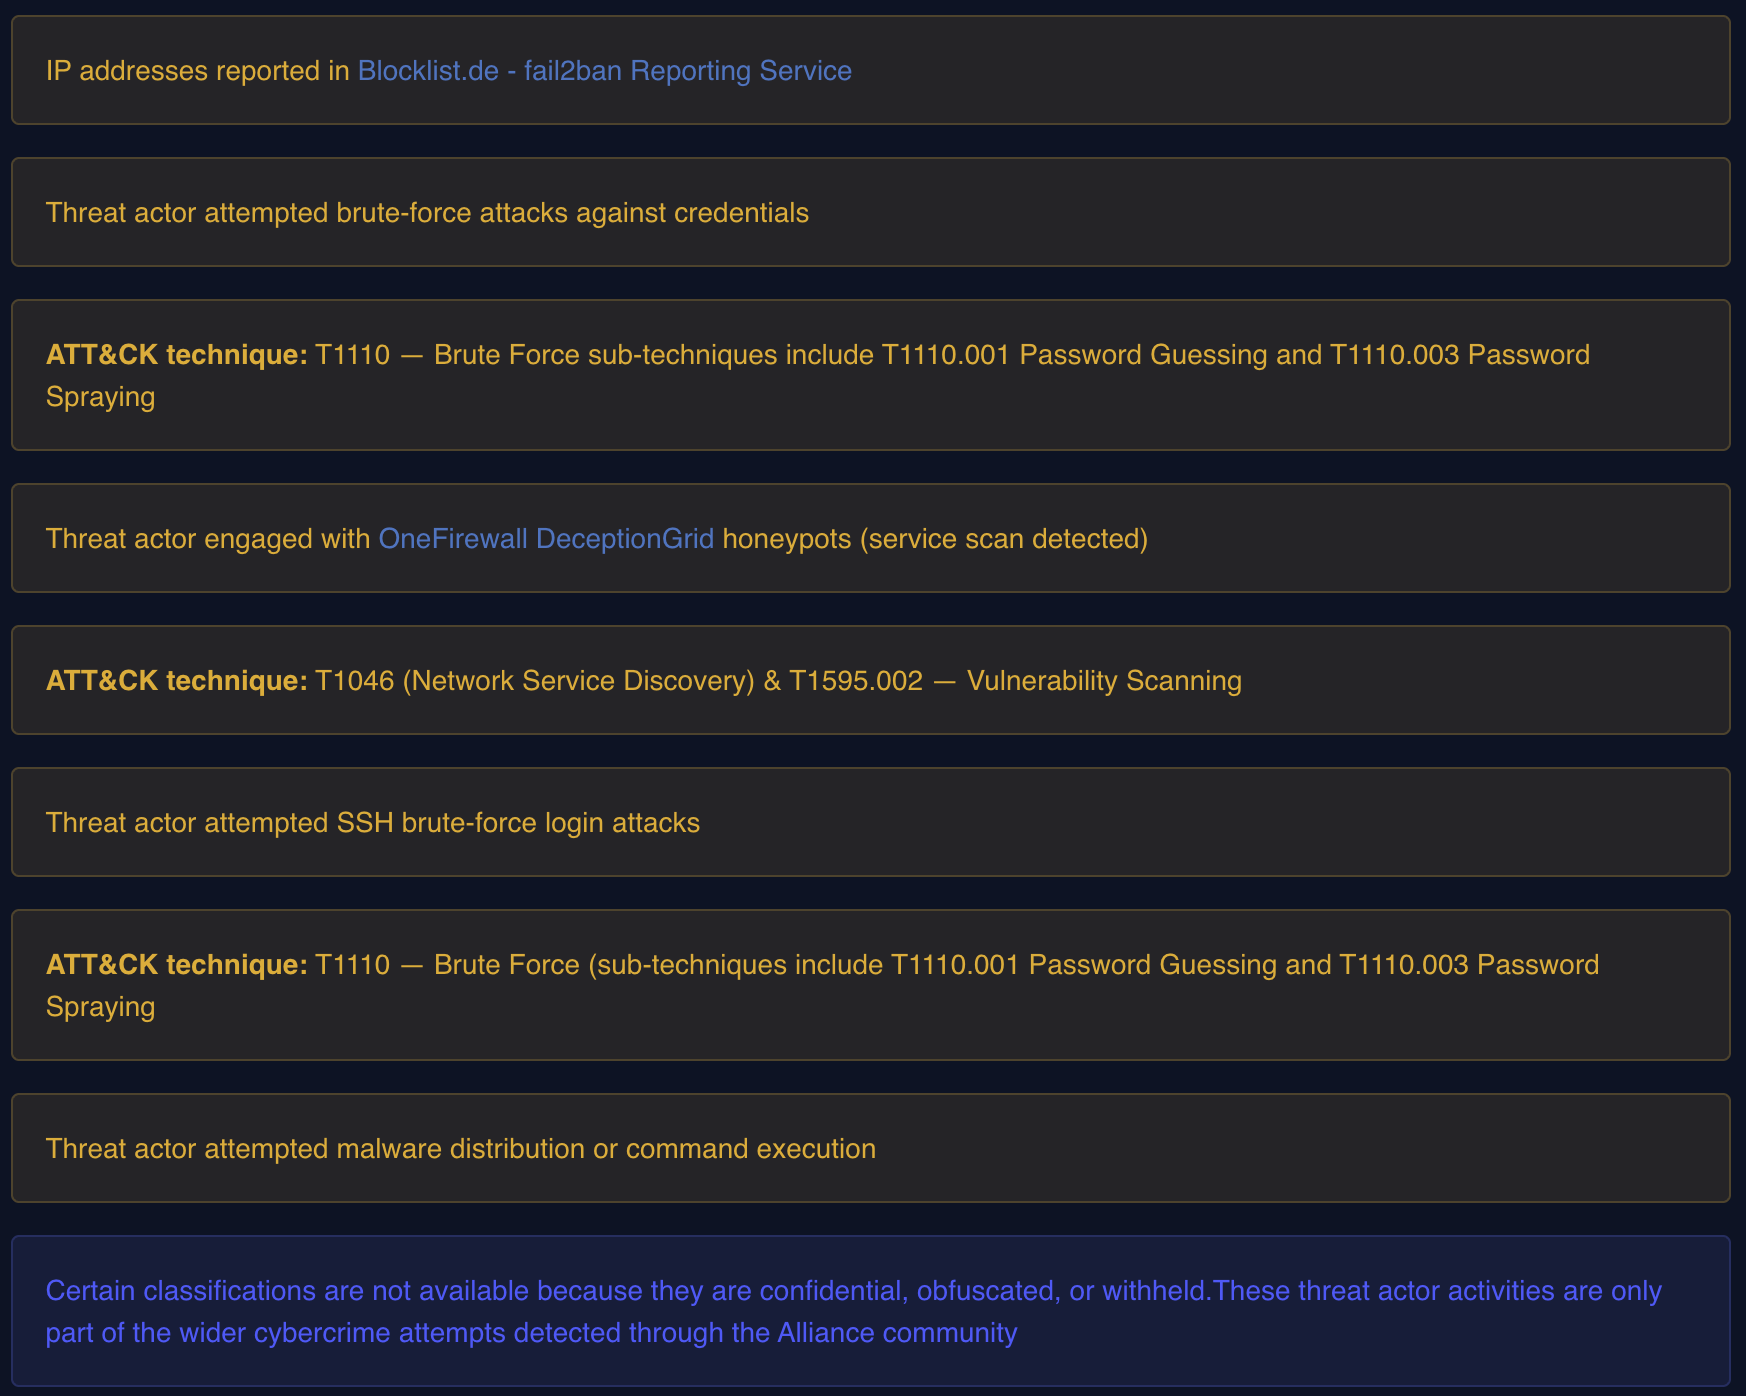
Attack destinations across alliance members and partners, mapped to MITRE ATT&CK tactics and techniques — from brute-force credential access to network service discovery — so your analysts see the behaviour, not just the IP.
Proud member of the Cyber Threat Alliance since 2020
OneFirewall shares vetted intelligence globally to strengthen collective cyber defence as a member of the Cyber Threat Alliance — an organisation working to improve the cybersecurity of the global digital ecosystem by enabling near real-time, high-quality threat information sharing among companies and organisations in the cybersecurity field.
CTA membership extends OneFirewall's telemetry reach beyond the alliance's own 290+ members into a wider global threat-sharing ecosystem — so a technique first seen by a CTA member on the other side of the world can still reach your firewall.