Your firewall is letting attacks through. We’ll show you which ones.
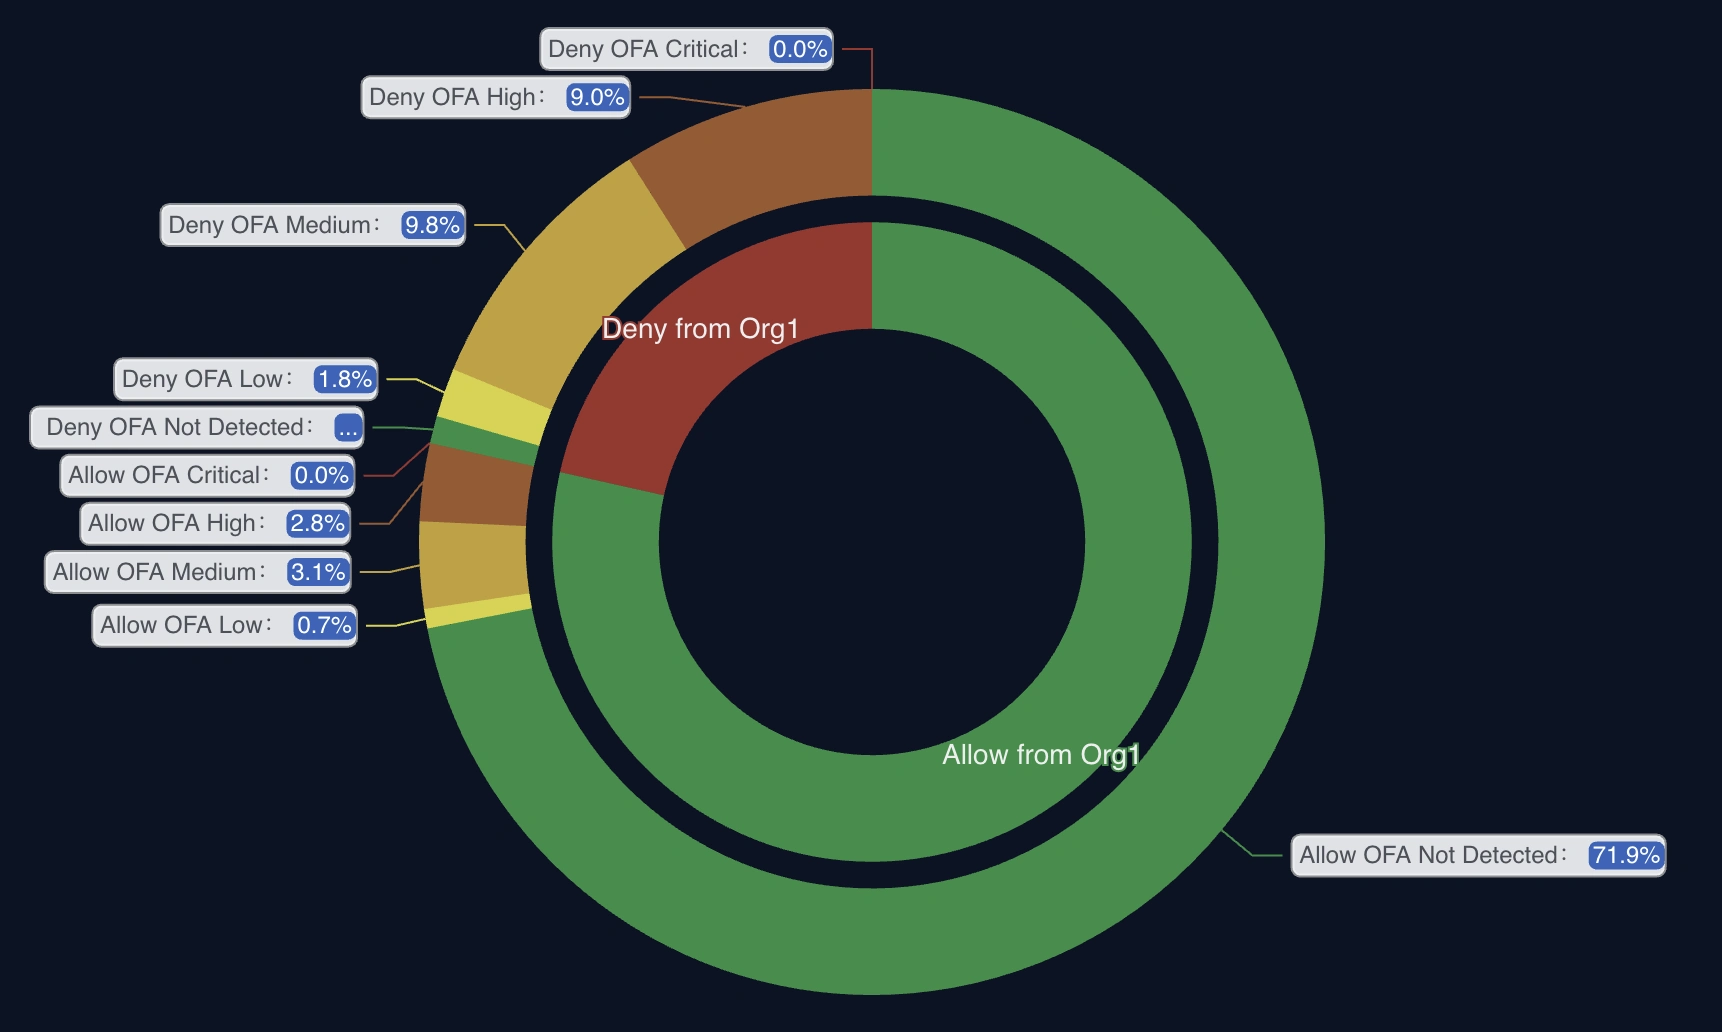
In a sample Proof of Value, 12% of the traffic a customer’s firewall allowed was malicious: 14,208 events in 10 days. OneFirewall checks your traffic against intelligence shared by 290+ independent security centres, then blocks those attackers on the firewall you already run.
No rip-and-replace. 166+ integrations, including Check Point, Fortinet, Palo Alto Networks and Sophos.
Free · Runs on a VM inside your network · No commitment
See what your firewall let through, using your own traffic
We run the OneFirewall platform on a VM inside your network. It checks your firewall logs against alliance intelligence and reports every attack that got through. Nothing leaves your perimeter, and there is no cost or commitment.
Kick-off call
A short call with our engineers to scope the PoV and agree which firewall logs to analyse.
A VM in your network
You deploy a containerised VM (min. 8 vCPU, 16 GB RAM, 300 GB disk) and point your firewall syslog at it. Your logs stay on the VM.
Your report
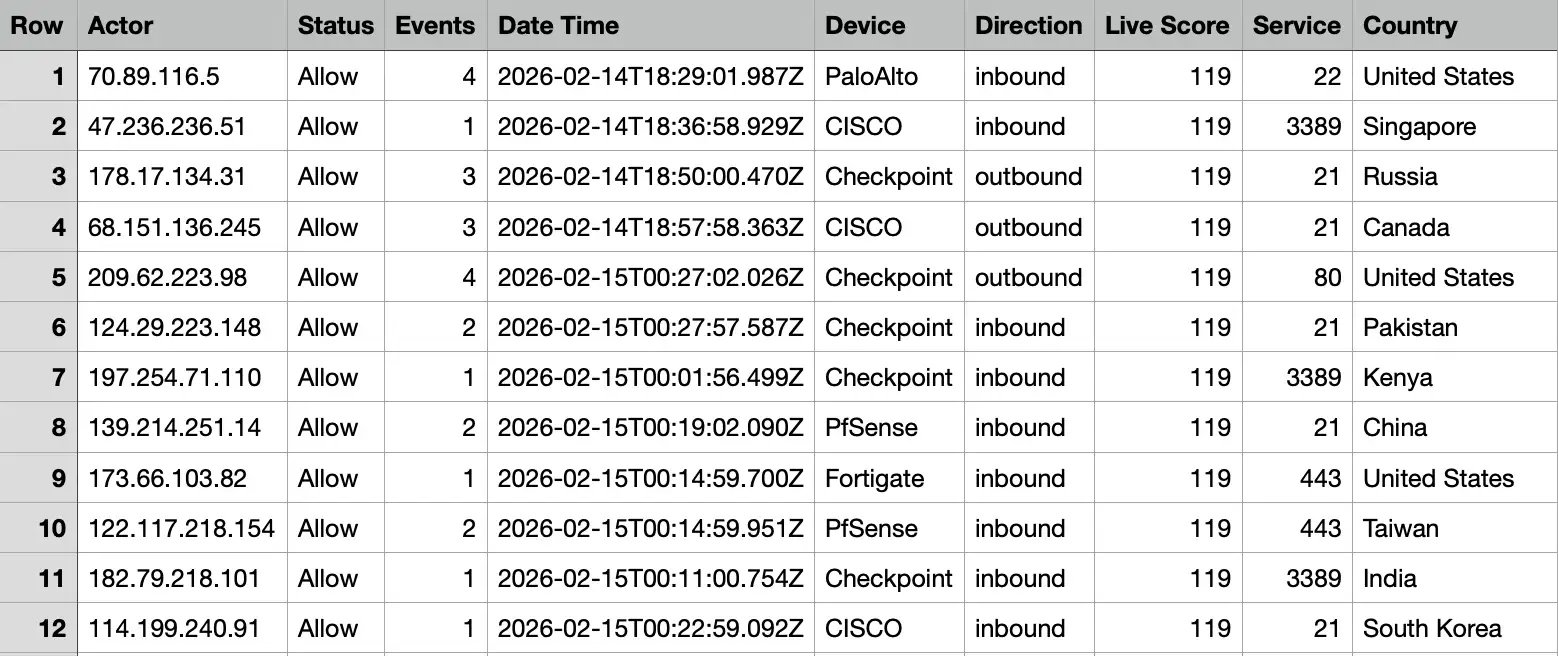
A PDF summary with your Crime Score, a CSV of every malicious connection your firewall allowed, and a cost-saving estimate.
A single platform for intelligence, enforcement, and assurance
Most vendors sell you one layer of defence. OneFirewall was built by combining all three — because collective intelligence is only as useful as your ability to act on it, and to prove it's working.
Collective Intelligence
IOC and CTI feeds crowd-sourced from 290+ alliance members, enriched with Crime Scores and MITRE ATT&CK mapping, delivered natively in STIX 2.1 / TAXII 2.1.
Explore Threat Intelligence →
Automated Enforcement
The WCF Agent pushes validated block-rules directly to your firewall, IPS, WAF or SIEM — no manual playbooks, no ticket queues, detection to enforcement in under 30 seconds.
Explore the Platform →
Security Assurance
Penetration testing, OpenSAMM maturity assessments, threat modeling and phishing simulation — validating that your defences hold up against a real adversary, not just a scanner.
Explore Security Assurance →Connected to the threat-sharing circle that already protects critical infrastructure
OneFirewall is a member of the Cyber Threat Alliance — the vetted group founded in 2014 by Fortinet, Palo Alto Networks, Symantec and McAfee to share threat intelligence across an entire industry, not just inside one vendor's customer base. Check Point and Cisco joined in 2017. CTA membership means OneFirewall's own alliance taps directly into that wider ecosystem.
What is OneFirewall Alliance?
OneFirewall Alliance is a UK-based cybersecurity company, founded in 2018 in London, that operates a SOC-to-SOC alliance: a crowd-sourced Cyber Threat Intelligence platform connecting 290+ independent organisations worldwide. Members share real-world attack observations, which are validated and enriched with a Crime Score (0–1000), MITRE ATT&CK mapping and STIX 2.1 / TAXII 2.1 formats, then enforced automatically across firewalls, IPS, WAF, SIEM and cloud controls in under 30 seconds. The platform integrates with 166+ firewall and security products.
Every data center, one shared nervous system
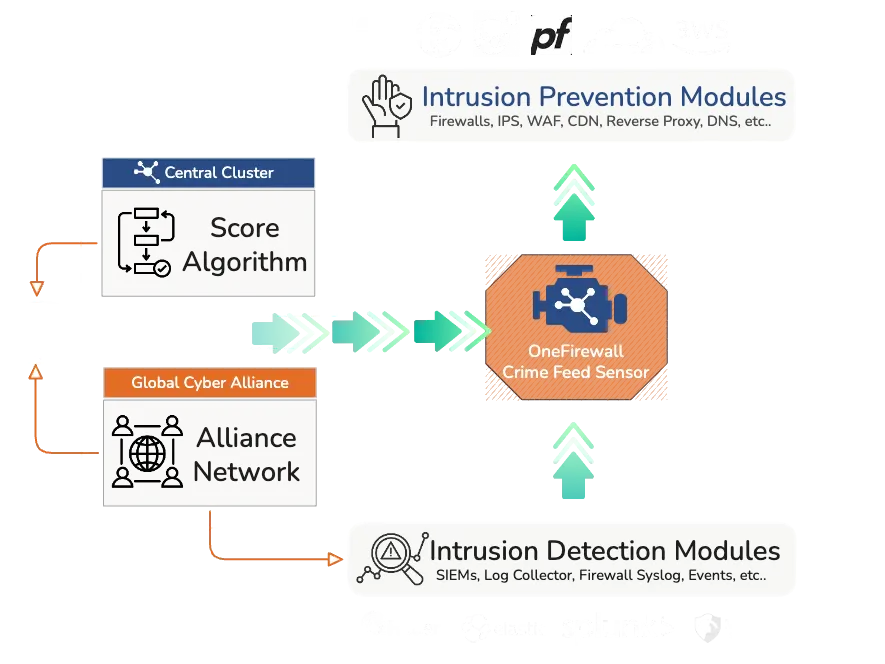
Each data center keeps running its own security products. The OneFirewall Agent sits alongside them, feeding intrusion data into a central rating engine — so a threat detected at Data Center A becomes a blocking rule at Data Center B, automatically.

35,000 daily attacks eliminated in 24 hours. Latency down 28% (client-reported).
A global SaaS platform running across Azure, DigitalOcean and GCP was absorbing 35,000 attacks a day, with nearly a quarter of all inbound traffic malicious. After deploying OneFirewall, unauthorised traffic dropped to zero while performance improved — the same alliance-wide defence network every member plugs into on day one.
Read the Full Case Study →35,000
Daily attacks before deployment (client-reported)
28%
Latency reduction
24h
Time to full resolution
12,000+
Daily feeds contributed back
“Every threat we identify collectively is an opportunity to protect another organisation.”
Juan Rivera, Executive Director, OneFirewall Alliance America. Joined the company in 2024. LinkedIn profile
Headquartered in London, with partners across North America, Europe, Asia and Latin America.
Alliance members and delivery partners spanning North America, Europe, South Asia, Southeast Asia and Latin America.
London, UK
OneFirewall Alliance LTD
Founded 2018
Manchester, UK
Red Five Technology Solutions
Venice, FL, USA
GTSAAS
Belgrade, Serbia
BondMesh DOO
Southeast Asia
Skylabs Solution India Pvt
Peru · Ecuador · Colombia
VLATAM
Frequently asked questions about OneFirewall Alliance
What is OneFirewall Alliance?
A UK cyber threat intelligence company. It runs a crowd-sourced alliance of 290+ independent organisations that share validated threat intelligence, enforced automatically on firewalls, IPS, WAF and SIEM platforms.
How fast is threat intelligence enforced?
According to OneFirewall's platform specifications, detection to enforcement takes under 30 seconds once an indicator is validated by the alliance.
Which firewalls and security platforms are supported?
OneFirewall lists 166+ firewall, cloud, WAF and SIEM integrations, including Check Point, Fortinet FortiGate, Palo Alto Networks, Sophos, AWS WAF, Google Cloud Platform, IBM QRadar and Splunk.
What is a Crime Score?
The Crime Score is a 0 to 1000 risk value assigned to IPs, domains, URLs and file hashes. It rises when several independent alliance members confirm the same threat, so volume from one reporter alone never triggers a block.
How is the intelligence shared in a standard format?
Intelligence is available as STIX 2.1 over a TAXII 2.1 server. STIX and TAXII are OASIS standards, so tools such as MISP and OpenCTI can consume it directly.
How do organisations get started?
Request a free Proof of Value, a risk-free assessment against your own infrastructure, or talk to our sales team. Data handling and certifications are set out on the Trust & Security page.