
Real-time security events your SIEM will love.
OneFirewall Alliance emits six categories of structured security events in CEF (Common Event Format) over syslog UDP — covering network threats, enforcement decisions, agent lifecycle, and MITRE ATT&CK-mapped observations, ready for any SIEM platform.
NET_EVENT — a network threat, fully described
Includes source/destination IPs, ports, risk assessments, threat scores, geographic data, and MITRE ATT&CK technique mappings — plus PUT_DECISION events logging every enforcement action with a complete audit trail.
CEF:0|OneFirewall|F3DAgent|4.0|
NET_EVENT|Network Threat Detected|8|
rt=1740000000000 src=185.220.101.45
dst=10.0.1.100 spt=44281 dpt=22
act=BLOCK cs1=847 cs1Label=crime_score
cs2=T1110 cs2Label=mitre_ttp
cs3=RU cs3Label=src_country
msg="SSH brute-force; TOR exit node"
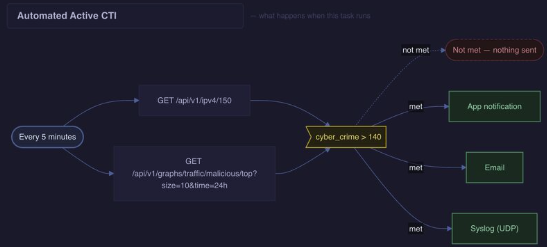
A polling loop, a threshold, and three places it can go
Every five minutes, the platform checks live IPv4 and malicious-traffic feeds against your configured Crime Score threshold. Nothing is sent while traffic stays under it. The moment it isn't, the event fires out to app notification, email, and syslog (UDP) simultaneously — no polling required on your end.
CEF over syslog is the universal language
Splunk
Configure a UDP syslog input. Events appear as parsed sourcetype=cef fields automatically.
Microsoft Sentinel
Use the CEF connector in Azure Monitor. Fields map directly to the CommonSecurityLog schema.
Elastic SIEM
Filebeat syslog input with the CEF processor module — events become ECS-compliant documents.
IBM QRadar
Add a Log Source of type Universal CEF. Events are normalised and categorised automatically.