
The assurance programme that finds what scanners miss.
A single, continuous security assurance programme — penetration testing, maturity benchmarking, threat modeling, continuous offensive security, code & infrastructure assurance, and phishing simulation — run by people who read the code, not just the CVE feed. One programme, one point of accountability, instead of five vendors' worth of reports to reconcile.
Most engagements start with one discipline — few stay there
Each one below is a standing capability inside the same programme, not a separate vendor relationship. Start wherever your risk is sharpest — we'll tell you honestly when another discipline matters more.
Penetration Testing
Hands-on, adversary-style testing of web, API, network, cloud, and wireless environments — validating what an attacker could actually reach and exploit.
OpenSAMM Assessment
OWASP SAMM-based maturity review of your software security practices, scored across governance, design, implementation, verification and operations.
Threat Modeling
Structured, STRIDE-driven analysis of architecture and data flows to surface design-level weaknesses before a single line of exploit code is written.
Offensive Security — Vulnix0
Continuous DAST, dark web exposure monitoring, and attack-surface testing powered by our offensive security platform, Vulnix0.
Code & Infra Assessment — AquilaX
SAST, software composition analysis, secrets detection, and infrastructure-as-code review delivered with our partner platform, AquilaX.
Phishing Simulation
Realistic, controlled phishing and spear-phishing campaigns that measure and improve the human layer of your defences.
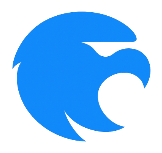
See exactly what was permitted, denied, and caught
A live 24-hour window from an AquilaX-protected environment: 30,467 parsed events, 1,343 blocked outright, and 8.2% of malicious traffic that was technically permitted by policy but still intercepted by OneFirewall — the gap a single scanning tool leaves open on its own.
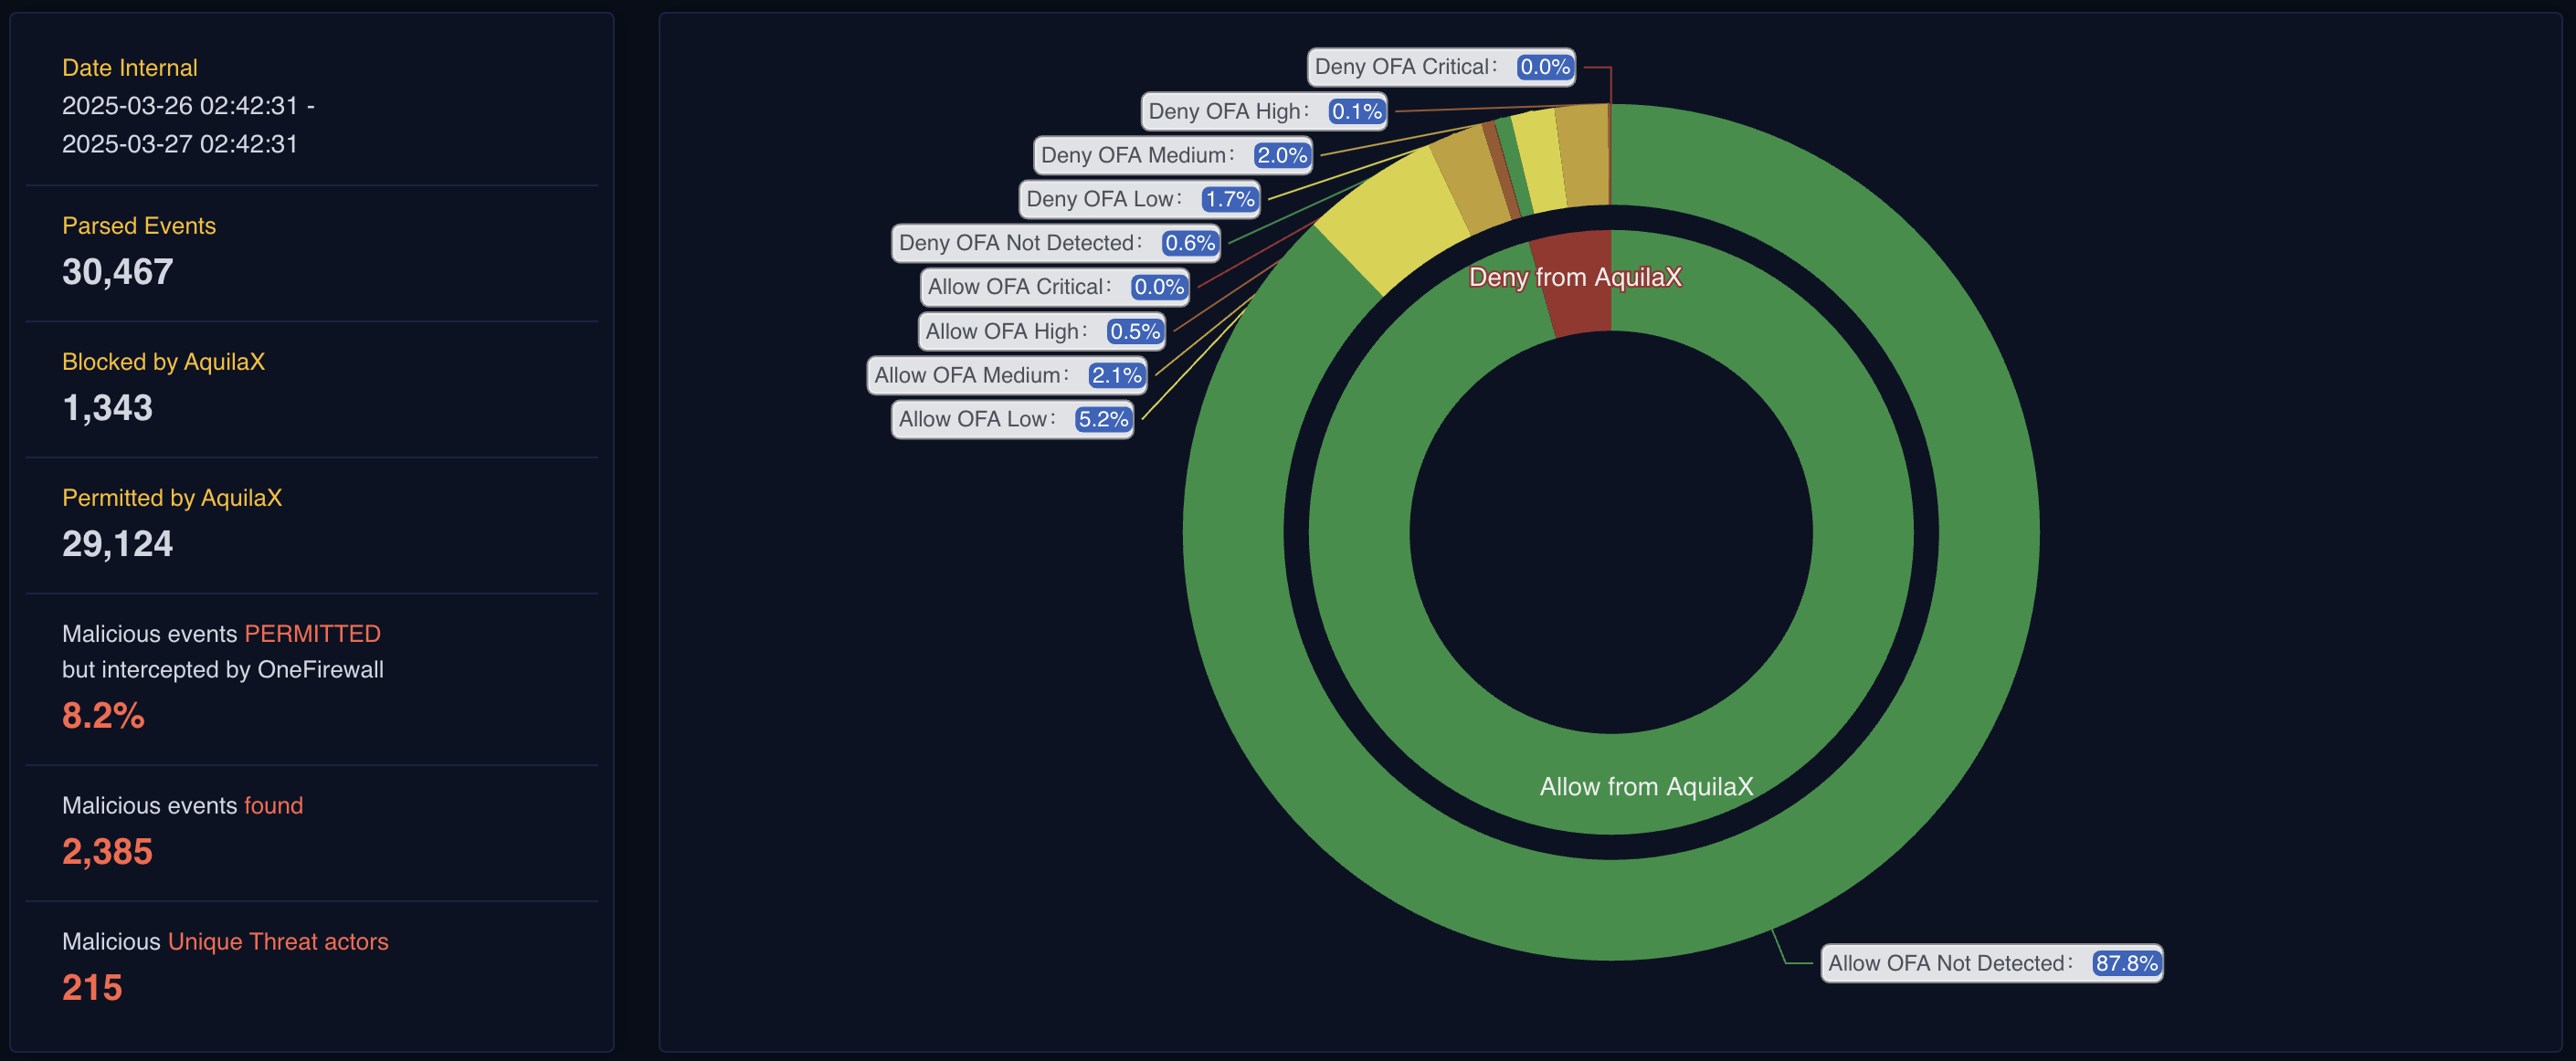
Every scan traced from parsed event to blocked threat
Vulnix0 classifies every parsed event by disposition and severity — clean traffic, denied traffic, and the contributed value of what the alliance already knew was dangerous — so you can see exactly where a single-tool scan would have missed a low-and-slow attacker.
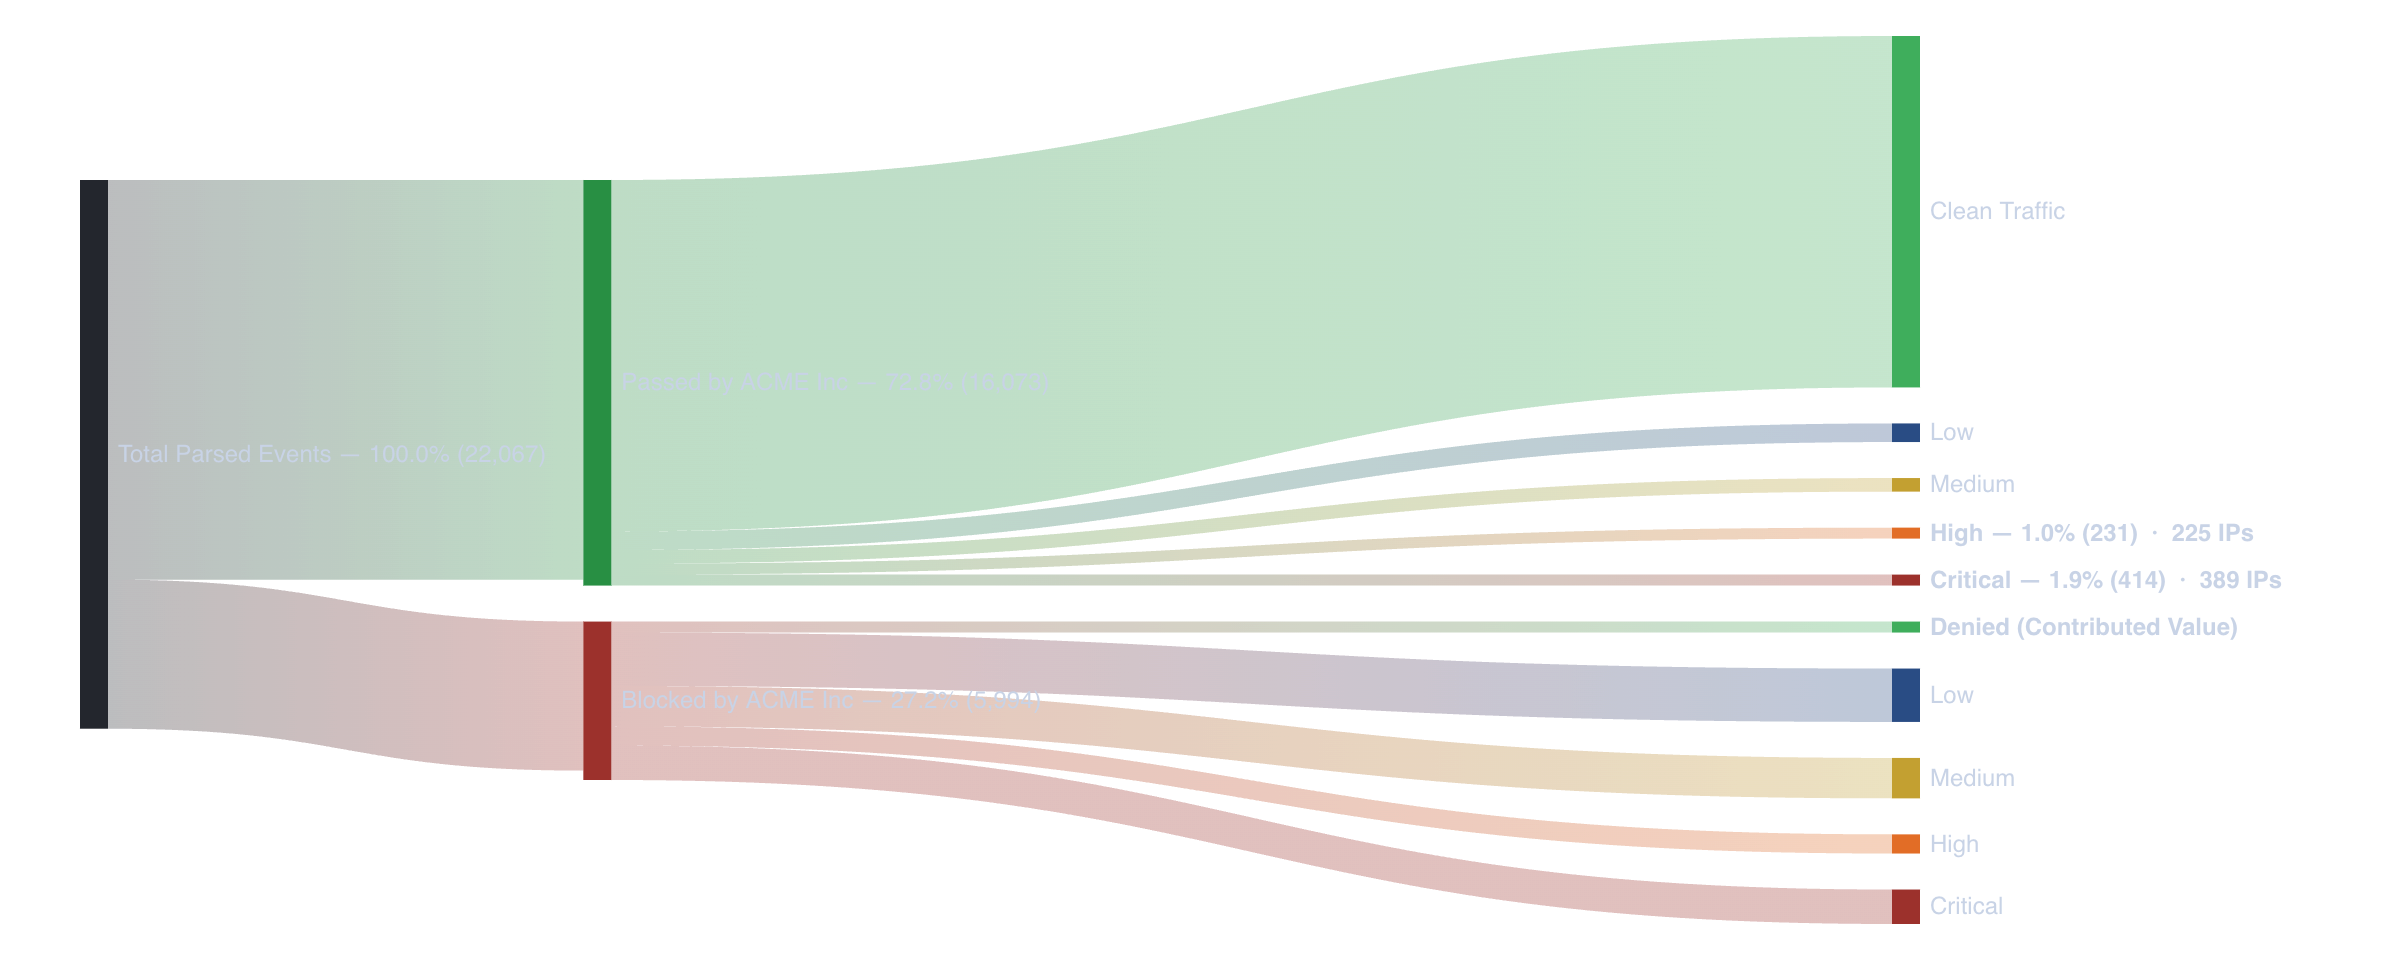
Attack-surface, DNS, TLS, and dark-web exposure in one scan
Vulnix0 runs continuous external reconnaissance against your own domains and infrastructure — DNS records, TLS configuration, open ports, and dark-web mentions — enriched with the same alliance threat context used across the OneFirewall platform.
Manual testing, not another scanner report
Automated scanners flag the obvious stuff and stop there. Our testers — OSCP and CREST CRT certified — manually work through your applications, networks, APIs, and cloud infrastructure the way an attacker actually would, chaining together issues a scanner would score as low-severity on their own.
- Web & mobile application testing (OWASP Top 10, OWASP ASVS)
- External & internal network penetration testing
- API security testing (REST, GraphQL, gRPC)
- Cloud configuration & workload testing (AWS, Azure, GCP)
- Wireless network and physical / red-team engagements on request
- One free retest included within 30 days of the report
A typical single-application engagement runs 5–10 working days on-site or remote, and closes with a technical report plus a 45-minute walkthrough with your engineering team — not just a PDF dropped in your inbox.
{
  "finding": "Broken Object Level Authorization",
  "category": "API5:2023 - OWASP API Security",
  "severity": "High",
  "cvss": 8.1,
  "endpoint": "GET /api/v1/invoices/{id}",
  "impact": "Any authenticated user can view
             another tenant's invoices",
  "remediation": "Enforce tenant-scoped
                   authorization server-side",
  "status": "retested-fixed"
}
How mature are your software security practices — really?
OpenSAMM (the OWASP Software Assurance Maturity Model) assesses how mature your software security practices are, not just your code. We review your organisation across five business functions: Governance, Design, Implementation, Verification, and Operations.
- Interview-driven assessment against 15 SAMM security practices
- Maturity scoring (0–3) per practice, benchmarked against industry peers
- Gap analysis with a prioritised, sequenced improvement roadmap
| Business Function | Typical Starting Score |
|---|---|
| Governance | 1.4 / 3 |
| Design | 1.8 / 3 |
| Implementation | 1.1 / 3 |
| Verification | 0.9 / 3 |
| Operations | 1.3 / 3 |
Lowest score, flagged first: Verification. Scores from a first-time assessment at a mid-sized SaaS client — most teams have never formally tested their own test coverage.